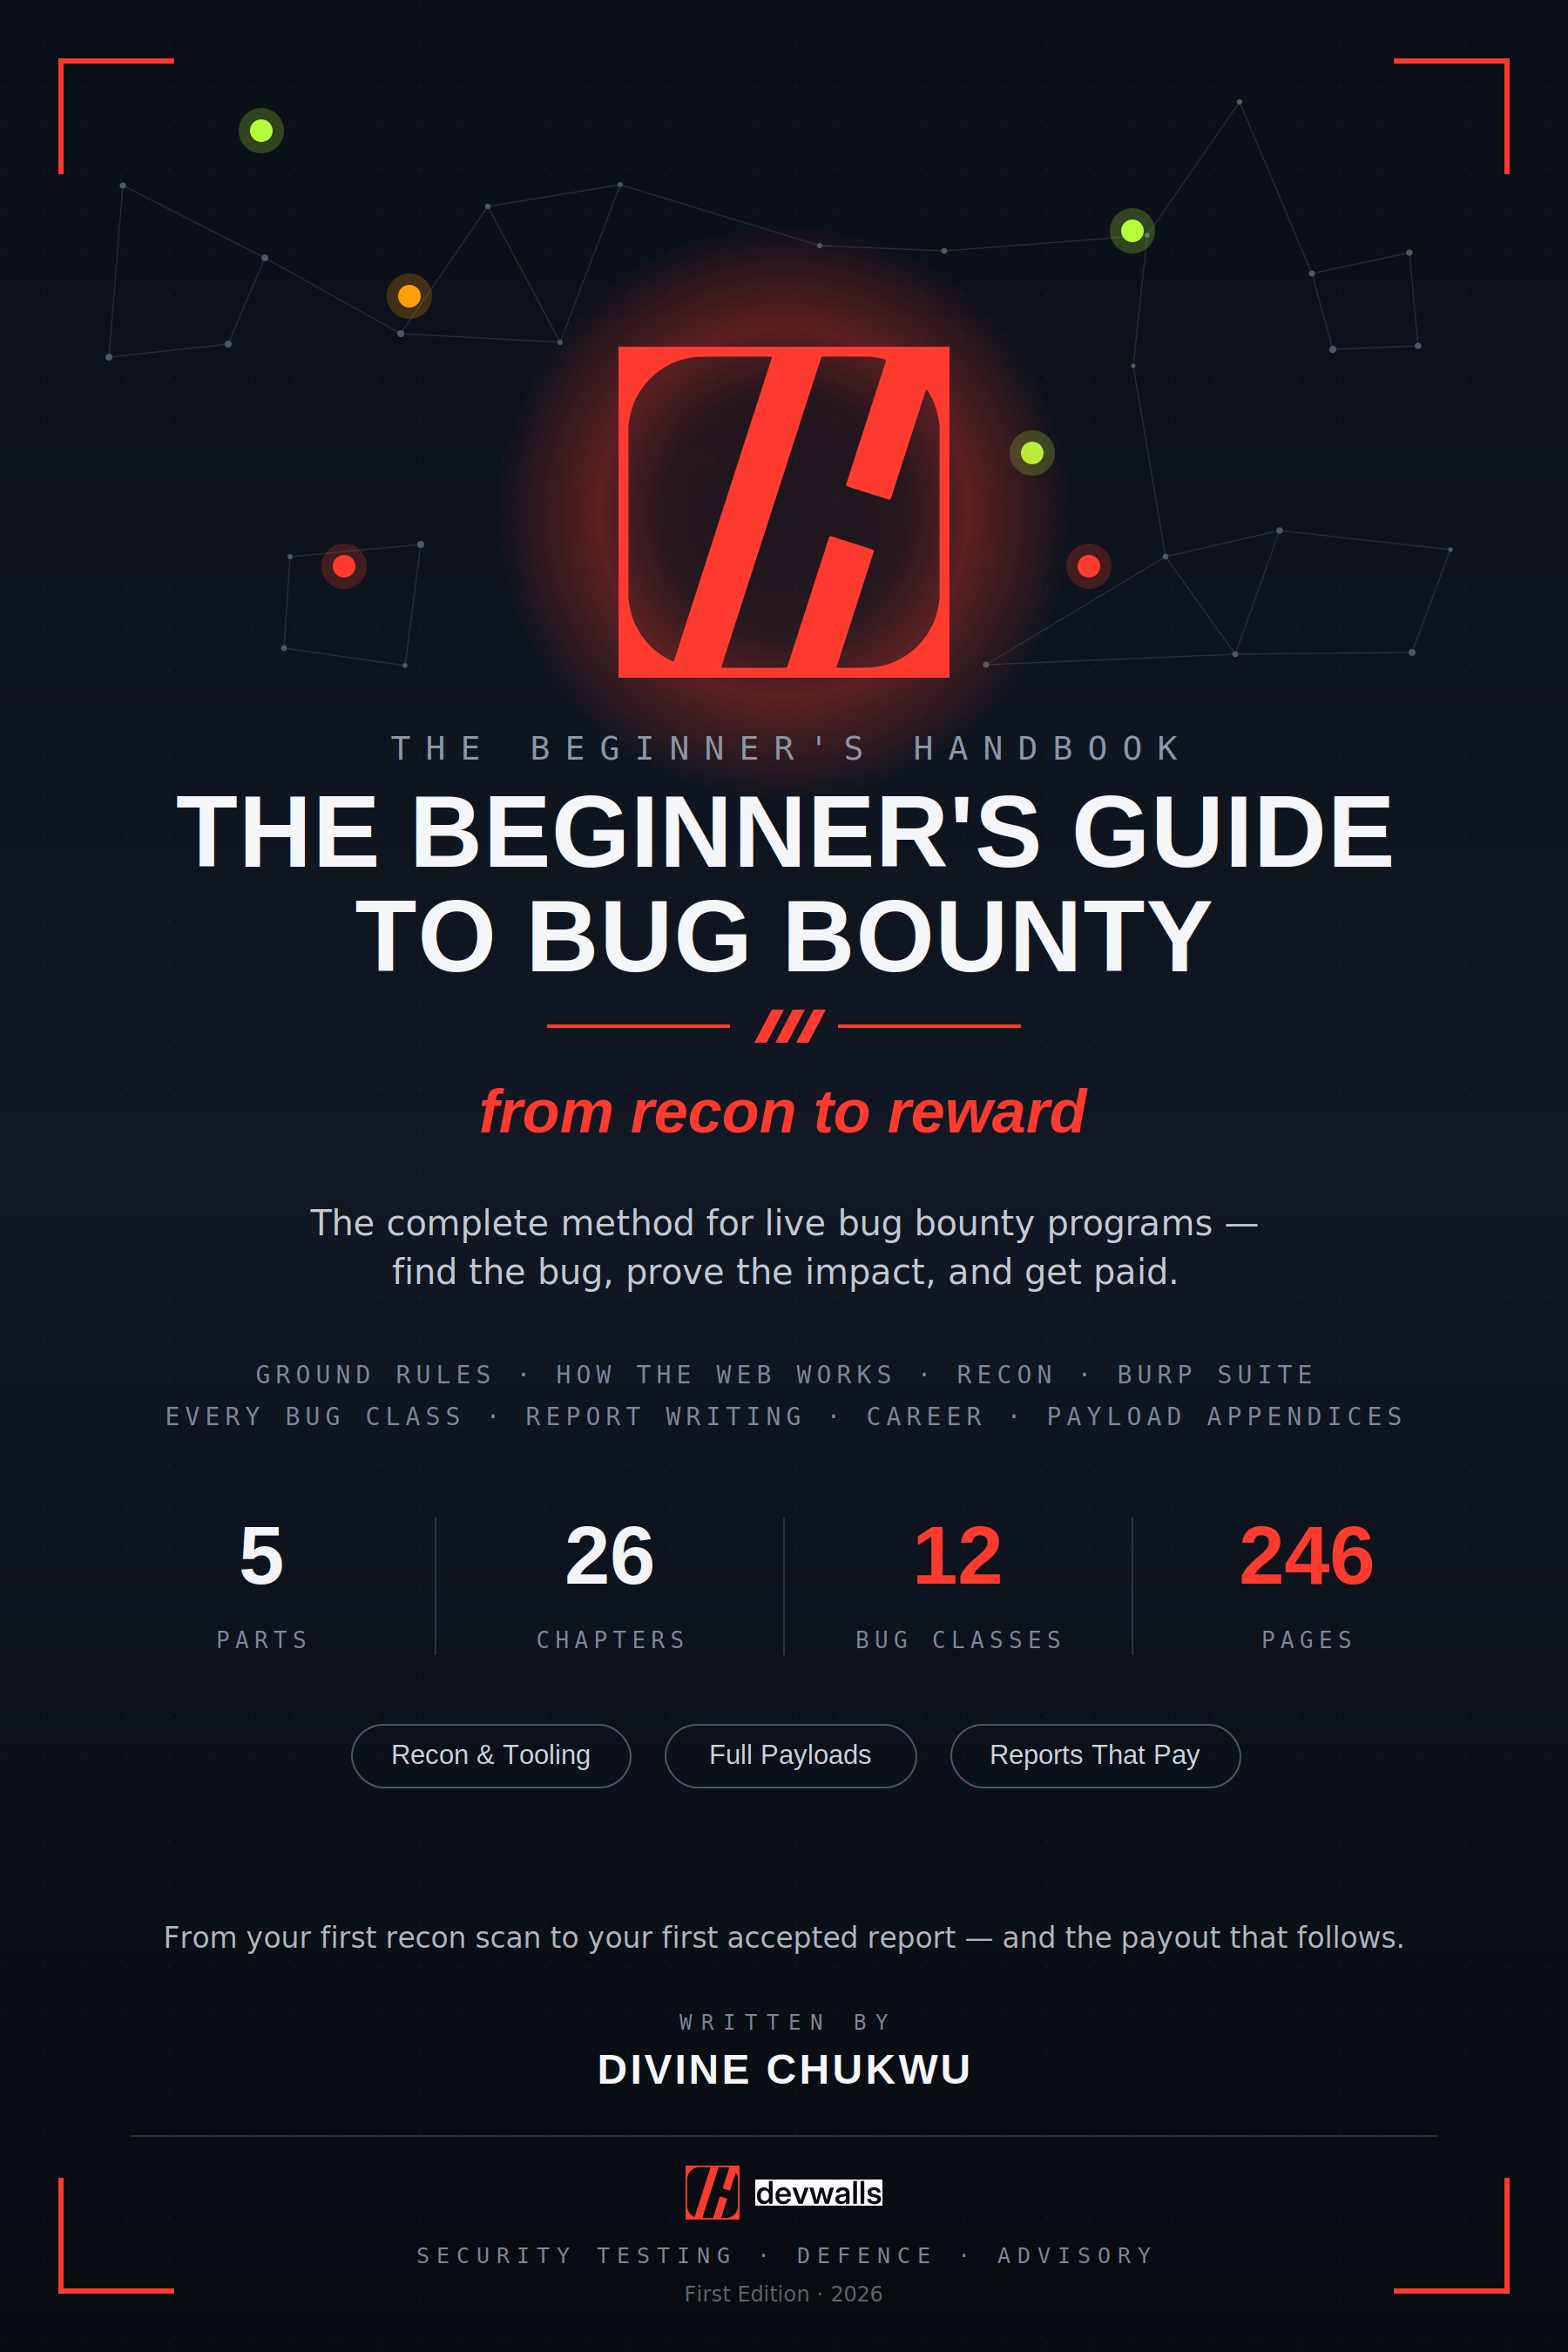
The Beginner's Guide to Bug Bounty
Most people who try bug bounty quit within three months — not because they can't find bugs, but because nobody taught them where to look, how to prove impact without crossing a line, or how to write the report that turns a finding into a payout. The Beginner's Guide to Bug Bounty is the book that fixes that.
Written by Divine Chukwu and published by Devwalls Security, this 246-page handbook takes you from zero knowledge to your first accepted report. No prior hacking experience required — just the willingness to work through it.
Inside, you'll learn:
- The honest economics of bug bounty — what beginners really earn, and how to pick unglamorous, under-tested programs where you can actually compete
- The legal ground rules — authorization, scope, and safe harbour across Nigeria, the UK, the US, and the EU, so you never put yourself at risk
- How the web really works — HTTP, sessions, and the browser security model that every vulnerability exploits
- A full recon and tooling workflow — Burp Suite from zero, subdomain enumeration, content discovery, and reading JavaScript to map an application
- Every major vulnerability class, with real payloads and step-by-step exploitation — access control & IDOR, XSS, SQL and other injection, SSRF, CSRF & CORS, authentication and JWT flaws, business logic and file upload, information disclosure, open redirects, path traversal, subdomain takeover, API & GraphQL testing, and race conditions
- The skill that actually pays — writing reports triagers accept on the first read, handling duplicates and rejections professionally, and climbing toward private, less-crowded programs
- A sustainable path — building a portfolio, reputation, and a real career in security
Plus four practical appendices: a payload & command quick-reference, a printable per-target methodology checklist, a full glossary, and three complete worked sample reports you can model your own on.
Every technique is taught the ethical way — prove, don't breach; use your own accounts; keep your proof-of-concepts harmless — because your reputation is the asset that pays you for years.
What you get: 246 pages · 5 parts · 26 chapters · 12 vulnerability classes · 4 reference appendices.
If you're serious about learning bug bounty properly — and getting paid for it — start here.